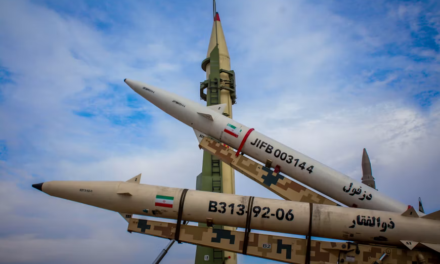
WASHINGTON DC. WA, November 2, 2026 — In response to the latest confirmed report from federal investigators on the largest cryptocurrency theft in history, which was attributed to North Korea-linked hackers, concerns are being raised about the potential use of these stolen digital assets to support the country’s weapons development program. The hackers attacked one of the world’s most significant exchanges and caused estimated losses of approximately $6.3 billion, far exceeding any other loss experienced during the previous decade.
How the Breach Unfolded
The Federal Bureau of Investigation is collaborating with industry collaborators in response to this theft, which blockchain analysis firms have indicated with high confidence was conducted by TraderTraitor, a hacking group that is believed to include North Korean operators who are also identified as the Lazarus Group and APT38. TRM Labs researchers stated that this breach is over four times greater than the largest recorded theft from an alternative exchange in 2025.
In recent years, cryptocurrency exchanges have been an ongoing focus of North Korean cyber-attacks. The hackers in North Korea have consistently used exploits against digital wallets, trading platforms, and blockchain bridges as a means of generating funds outside of the normal international financial system. However, this most recent theft is a significant increase in both the size and complexity of the attack when compared to prior occurrences.
A Pattern of Escalating Heists
North Korea’s activity in stealing cryptocurrency has significantly increased since 2017. The United Nations Panel of Experts estimated that North Korea stole approximately $3 billion in digital currency from 2017 through the mid-2020s. This funding was used to support its weapons programs. In 2022, independent researchers found that North Korean actors were responsible for stealing over $2 billion in cryptocurrency.
In addition, the hacking infrastructure that supports these attacks has grown substantially. There are estimates that there are several thousand highly-skilled cyber warfare personnel working for North Korea’s cyber warfare program. They operate out of numerous specialized units. Because of their sheer size, North Korea can continuously target cryptocurrency infrastructure despite the fact that exchanges are investing so much money into improving their cybersecurity.
Why Crypto Remains a Target
Because of how easily and quickly you can move and launder stolen money using digital currency exchanges, they are a primary target. As compared to traditional banking, where you can transfer funds internationally with relative ease but must comply with the laws of each country, cryptocurrency transactions provide an opportunity to avoid many of the international sanctions enforcement mechanisms that would normally hinder recovery efforts. These two qualities – speed and the ability to operate without revealing your identity – have made digital currency exchanges a consistent vulnerability even though there have been numerous warnings regarding them over the past few years by various government agencies.
Previous warnings issued by the FBI encourage companies in the cryptocurrency space to monitor blockchain transactions closely for indications that stolen assets may be readied for withdrawal. In previous investigations, the FBI was able to identify particular wallet addresses associated with North Korean actors prior to those funds being laundered completely. This type of initial tracking continues to remain essential to the Bureau’s efforts to respond to this most recent, much larger theft.
What Happens Next
While the FBI has not provided a timeline on when they will be able to get back all of the money stolen, the agency says that the case is still open with international law enforcement agencies working on it. Following the attack, many cryptocurrency trade groups are now calling for better, more comprehensive industry-wide security measures, saying that each exchange alone cannot fight off a threat as large as this one. Many regulatory authorities around the world are likely to look at how each exchange protects its customers’ assets and data after seeing this incident occur.
The theft is currently a stark example of the extent that state-sponsored hacking plays in the cryptocurrency world. Analysts believe that investigations into the theft will lead to increased scrutiny on the security measures taken by exchanges over the next few months. It is still unclear if this historic attack will result in any long-term changes to how exchanges protect their customers’ money.
The techniques used by North Korea’s hacking units have evolved significantly through multiple operations, according to cybersecurity professionals. In other words, they have been able to refine their methods based on what worked and didn’t work in prior breaches. For example, their focus has shifted from direct exchange intrusion to more complex methods such as compromised software updates and employee targeted social engineering. This change in methodology has increased the difficulty of detecting the activities of these groups for most security teams regardless of resources.
Treasury Department officials have already taken action against digital wallets and shell corporations associated with North Korea’s cyber-attacks; however, enforcement of international sanctions on a decentralized and borderless technology will remain challenging. This most recent attack should lead to renewed requests for increased international cooperation to identify and freeze the proceeds from these types of attacks prior to being able to fully launder them.